


Part 1
OcientAIQ™ for Cybersecurity
Every threat leaves evidence.
Search every byte of it.
Affordably retain years of full-fidelity network flow, so your security team can investigate across your entire network history, alongside the SIEM and SOAR tools you already run.
Full fidelity. Full history. One foundation.
OcientAIQ is the analytical data foundation underneath your SIEM, built for threat hunting and investigation.
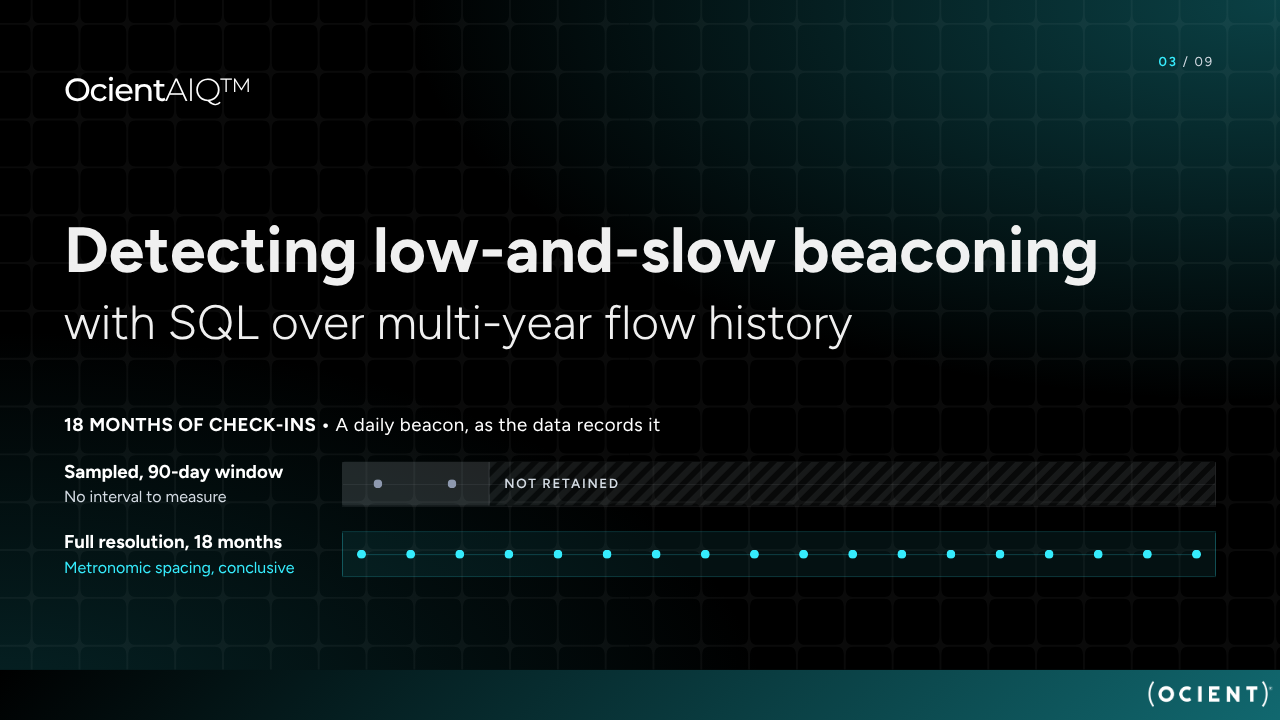
Full fidelity, no sampling
Analyze every record at full resolution, with no forced sampling or pre-aggregation.
Years of history, searchable in seconds
Query petabytes of current and historical data interactively, with indexing that keeps searches fast as data grows.
Every source, one query
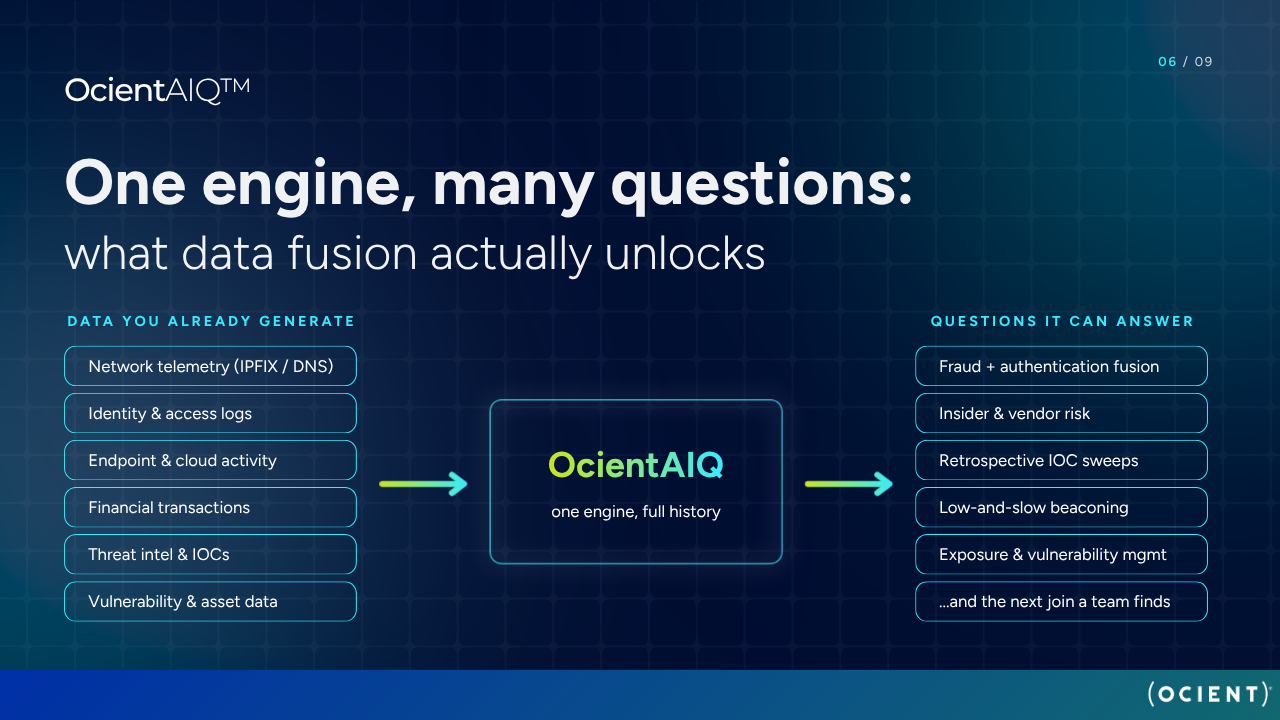
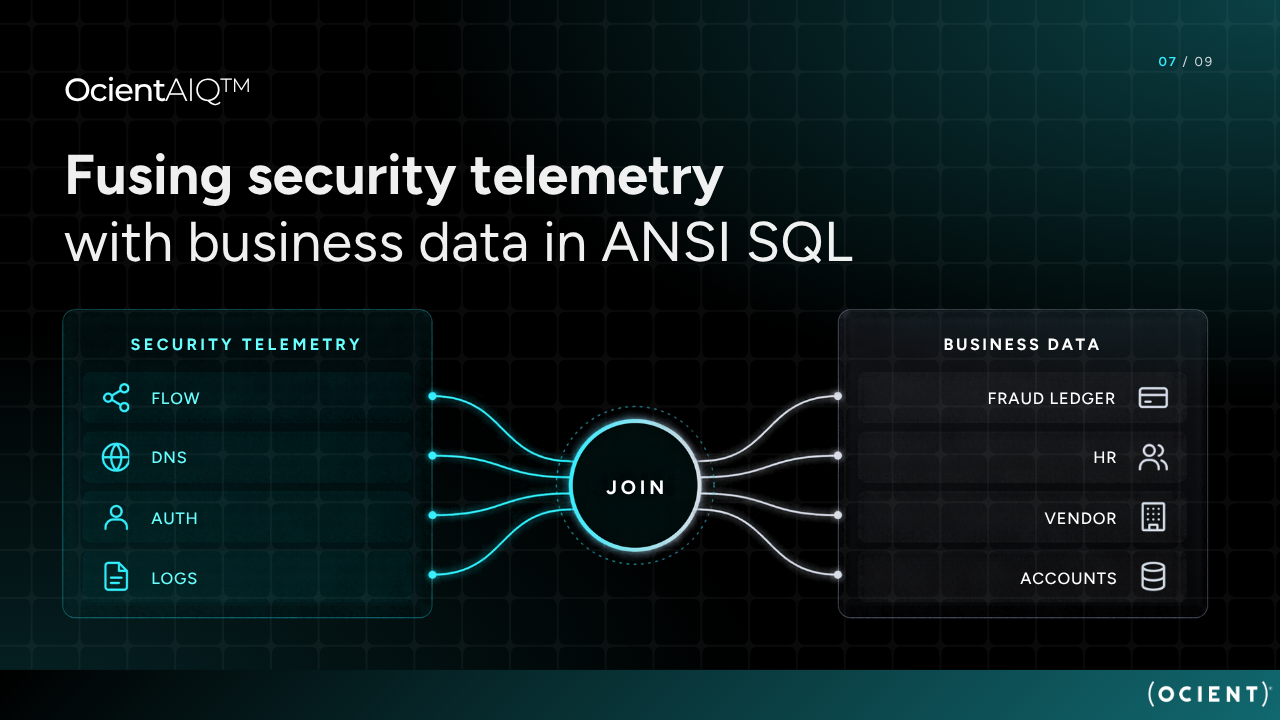
Correlate network, identity, endpoint, cloud and threat-intelligence data underneath your existing SIEM, SOAR and CTI tools.
Governed and auditable
Every result shows the query behind it. Every query is logged. Access is governed by roles and one semantic model.
Deploy anywhere, scale predictably
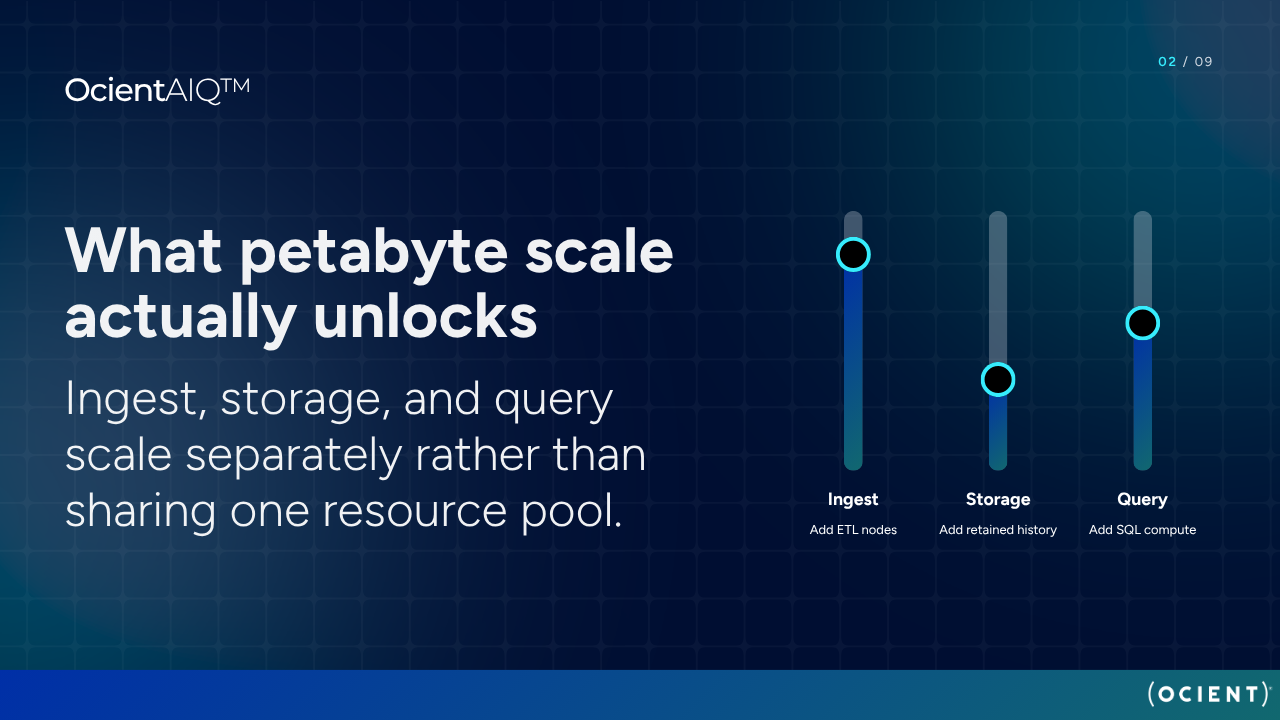
On-premises, private cloud, hybrid, GovCloud or air-gapped. Scale ingest, storage and concurrency independently, at fixed capacity.
Where it fits
A network telemetry layer alongside the stack you already run
Taps and probesYour telemetry
Routers and flow probes
Network flowsIPFIX and NetFlow
Resolvers and DNS taps
DNSEvery query and response
Firewalls and edge devices
Edge flowTraffic from devices that run no agent
Core signaling probes
Core signalingDiameter, for carrier networks
OcientAIQ for Cybersecurity
Keeps every recordFull fidelity, no sampling
Detects in placeSQL detections across full history
Governs accessRoles and one semantic model
Logs every queryWho searched what, and when
In your environment, on your infrastructure
Your stack, unchanged
SIEM and SOARAlerts and evidence via SQL or export
SOC analystsHunt in the app or any SQL tool
AI and data platformDetections as MCP tools
Reporting and BIStandard SQL over JDBC
See it in action
Hunt across every record at interactive speeds
01
Keep every recordFlow, DNS and other security feeds in one database, at full resolution.
02
Detect where the data livesSQL detections for DDoS, DNS tunneling, C2 beaconing, scans and fast flux run directly on the full history.
03
Ask in plain languageAn AI analyst answers from a governed semantic model of your network data, and logs every query it runs.
Ask OcientAIQ
Which hosts are phoning home?
Questions from the OcientAIQ network analyst demo, run on synthetic data.
Industries
Built for the environments you protect
TelecommunicationsCarrier-scale telemetry, kept unsampledUnsampled flow and DNS stay searchable across the full window, including edge devices that run no agent.Carrier-scale flowEdge devicesNetwork resilience
Financial servicesInvestigate across years of network evidenceFull-fidelity flow and DNS in one layer you can query in SQL.PCI DSSDORANYDFS Part 500
GovernmentNetwork history that stays searchableLong-horizon network search on infrastructure you control, including GovCloud and air-gapped.OMB M-26-14GovCloudAir-gapped
HealthcareCyber safety is patient safetySearchable network history across connected clinical and operational environments.Network visibilityRansomware forensicsHIPAA
EnergyOne view across IT and OT networksIT and OT network flow correlated in one place, across the full history.NERC CIPIT/OT convergenceGrid resilience
Insurance and enterpriseLarge networks, full historyNetwork evidence correlated across your full history.Third-party connectionsBeaconingCorrelation
 Webinar with Carahsoft
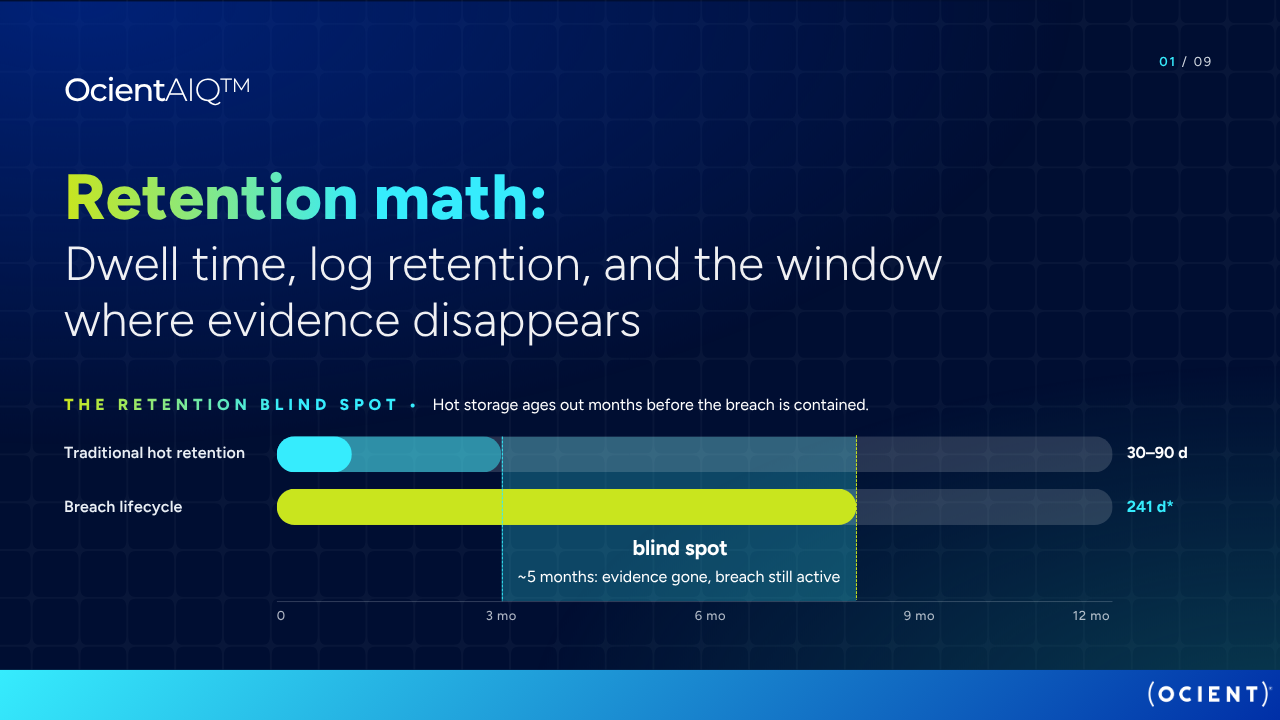
When the evidence expires
Closing the gap between attacker dwell time and searchable retention
FeaturingMatt McCraithPrincipal Solutions Architect, Ocient National Security Solutions
Register now Wed, Nov 18 · 2:00 p.m. ET · 60 min · Online
What today’s logging and retention requirements ask of security teams
How storage and query economics drive retention decisions
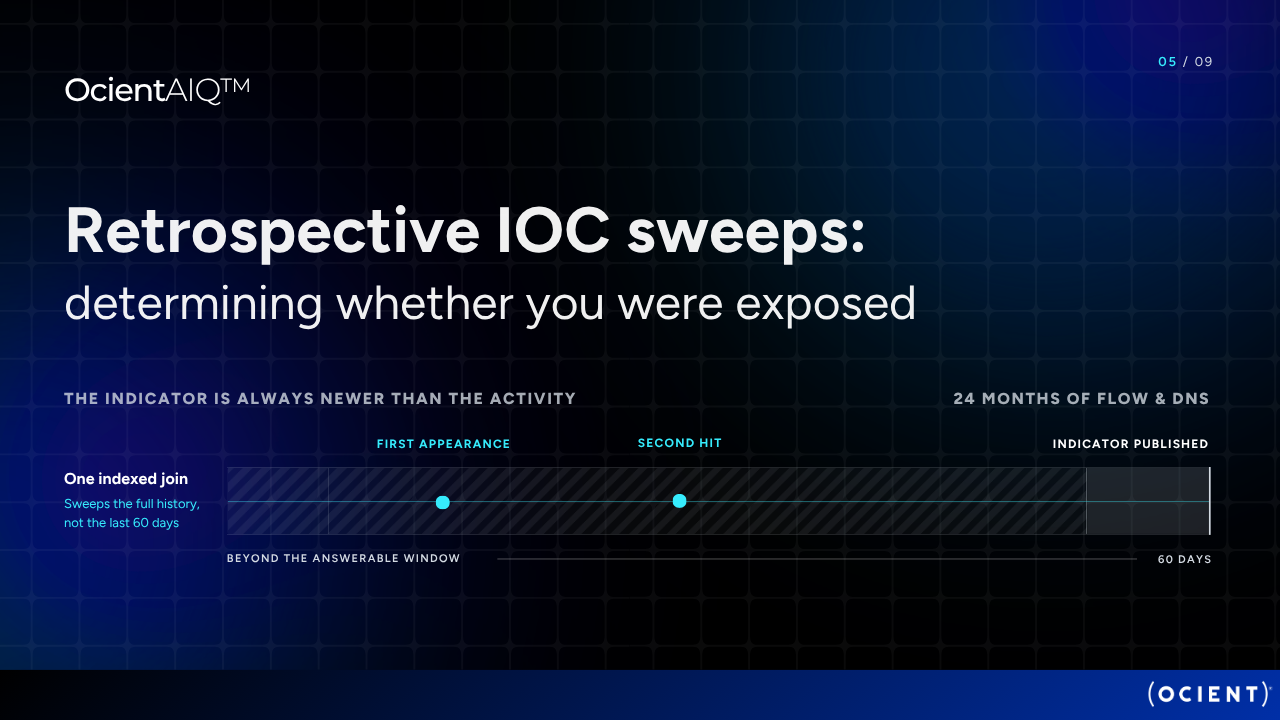
Retrospective threat hunting across a multi-year dataset, live
Adding long-horizon search without a SIEM migration
The cybersecurity series
Part 9
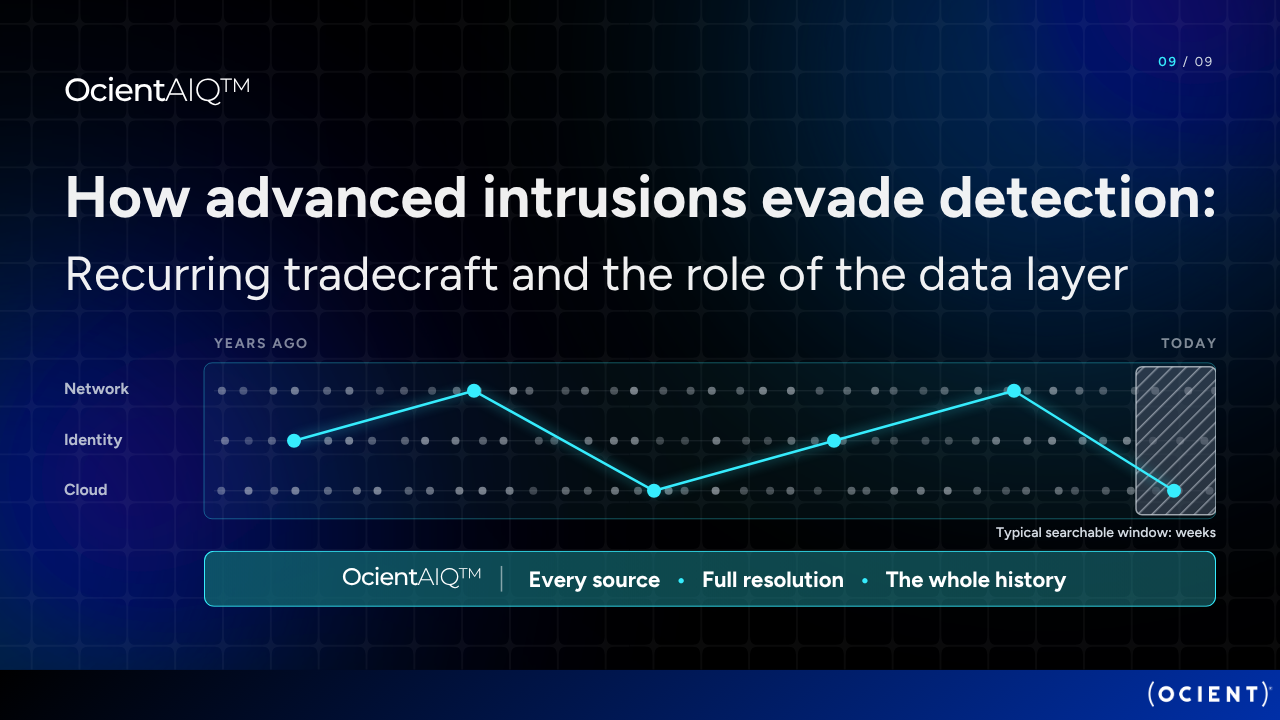
How advanced intrusions evade detection: Recurring tradecraft and the role of the data layer
What if you could put your full network history to work?
With OcientAIQ, you can.